Govern Your AI Coding Fleet.
Stop Token Bleed. Unify GitOps Rules. Automate Compliance.
Give your engineers the freedom to code with Cursor, VS Code, IntelliJ, and Claude Code while maintaining full corporate control. Cut up to 74% in wasted model spend, synchronize repository rules across microservices, and produce tamper-proof audit trails for the EU AI Act and DORA.
 Antigravity
 Copilot
 VS Code
 IntelliJ
 Cursor
 Visual Studio
 Claude
 Gemini
Antigravity
Copilot
VS Code
IntelliJ
Cursor
Visual Studio
Claude
Gemini
The Developer AI Wild West
The hidden risks of running unmonitored local AI agents across engineering workstations.
The Black-Box Blindspot
Cloud gateways and proxies inspect only network payloads. They are completely blind to the local filesystem execution occurring on developer laptops.
The Exfiltration Threat
Recursive agent loops searching directories can autonomously read SSH credentials (`~/.ssh/id_rsa`) or local configuration configs, and stream them to external API endpoints.
The Context Waste Drain
Local agents frequently ingest massive build caches and redundant project directory files, causing "lost-in-the-middle" attention degradation and inflating token spend.
Guideline Drift
AI assistants generate code loops without loading version-controlled security templates, resulting in silent syntax vulnerabilities and policy drift.
The Governance Framework
How Sprawl governs agent workloads without introducing developer latency.
Directory-Scoped Context
Restricts agent file access to targeted active project filesystems via local, directory-scoped MCP servers, preventing access to host credentials and private configuration folders.
Out-of-Band Telemetry
Logs session timelines and agent actions out-of-band directly to a self-hosted auditing dashboard, ensuring 100% data residency inside your corporate network.
GitOps-Driven Audits
Enforces workspace rules via version-controlled templates in Git. Custom pre-commit gates evaluate session telemetry logs, blocking the commit if model rules or safety constraints were bypassed.
The Telemetry Cockpit, Running Now
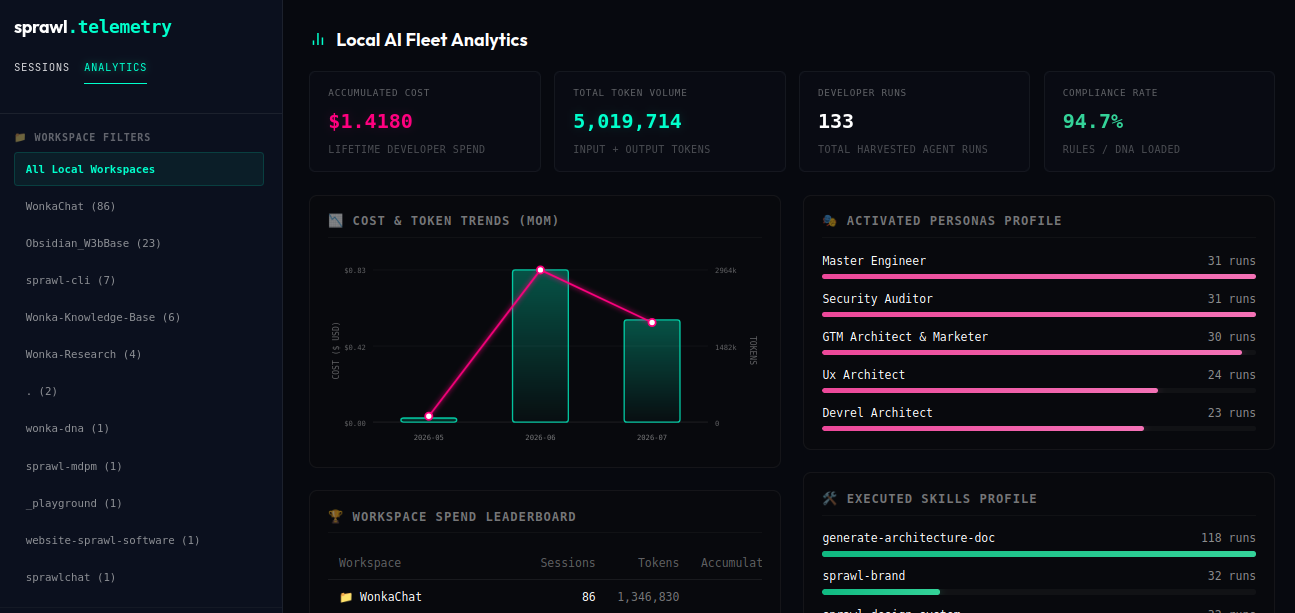
Real fleet analytics collected out-of-band from local developer workstations. 133 agent sessions. 11 workspaces. Zero editor lag. Zero cloud dependency.
Fleet-Wide Compliance & Spend Auditing
Automatically harvest telemetry from all active developer workstations to get a unified view of your organization's AI usage. Monitor spend, token volume, and policy compliance in real-time.
- ✓ 133 active agent sessions audited across 11 local workspaces.
- ✓ $1.4180 accumulated spend tracked dynamically behind the firewall.
- ✓ 94.7% rules compliance rate across all active developer environments.
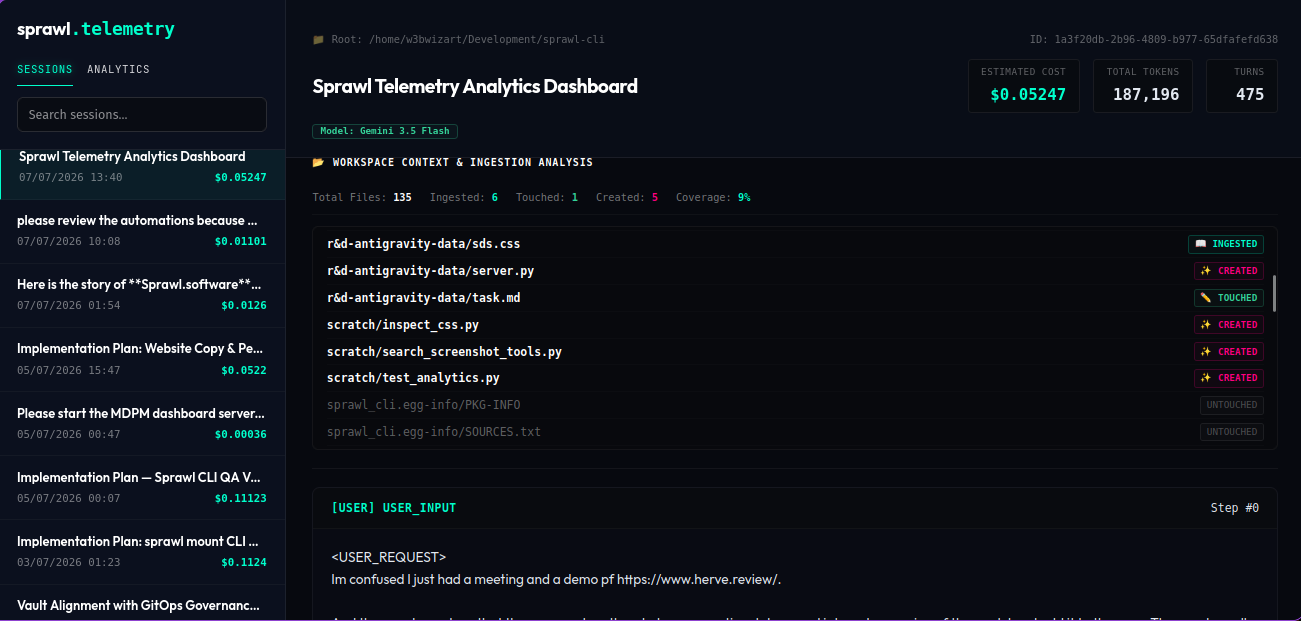
Deep-Dive Session Auditing
Inspect any individual agent run to see the exact context files ingested, token count distribution, and estimated cost breakdown. Drill down to prevent context bloat and optimize token efficiency.
- ✓ Per-run cost estimating maps model price tokens to actual dollar spend.
- ✓ Context coverage analysis tracks precisely which files (e.g. 6 of 135) were sent to the LLM.
- ✓ Turn-by-turn volume metrics show token usage over 475 reasoning steps.
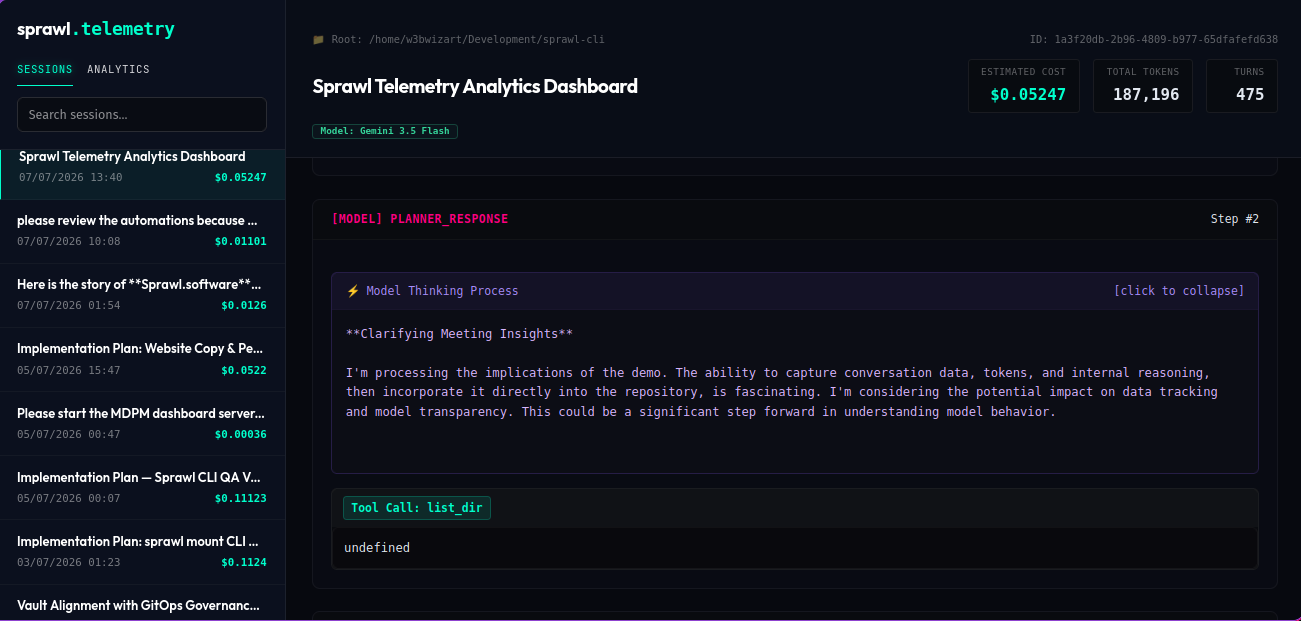
Agent Reasoning & Tool Auditing
Capture the agent's internal thinking process and monologue before it executes a command. Audit the exact parameters, inputs, and outputs of local CLI tools and script runs.
- ✓ Thinking monologue logs reveal model intent, reasoning steps, and safety checks.
- ✓ Zero-overhead auditing extracts local histories with zero developer latency.
- ✓ Audit-ready evidence logs mapping directly to SOC2 compliance criteria.
Workspace Control Cockpit
How Sprawl satisfies the distinct requirements of your organization.
Secure Local Fencing & Compliance
Prevent local model tools from accessing host credentials. Sprawl encapsulates process namespaces, guaranteeing that agent actions remain directory-locked and fully logged.
- ✓ Directory path-scoping via scoped MCP servers
- ✓ Intercept path-traversal reads outside active folders
- ✓ Full session audit logs, feed directly into your SOC2 evidence packages
Enforced Security Controls
Workstation-level constraints applied instantaneously upon initialization.
- Filesystem Scoping: Directory-Locked
- Credential Shielding: ~/.ssh Interception
- Audit Logging: Zero-Overhead Local
- Rules Compliance (POC): 94.7%, 5.3% gap
- Audit Trail: SOC2 Evidence-Ready
Simple, Predictable Pricing
Start free with your team under BSL 1.1. Upgrade for local FinOps telemetry, branch cost attribution, or centralized multi-repo fleet governance.
Core Runtime
Solo developers & engineering teams up to 5 developers.
Free forever under BSL 1.1
- Core CLI engine (
sprawl graft,bind,doctor) - Sub-4ms in-memory path validation & boundary fencing
- Universal IDE adapters (VS Code, IntelliJ, Cursor, Visual Studio)
- Declarative
.agents/GitOps rule synchronization - 100% offline, zero cloud calls & zero external dependencies
Local FinOps & Power
AI consultants, boutique agencies, and performance-minded power users.
€228/year billed upfront (excl. VAT)
- Everything in Community included
- Local Telemetry & Token FinOps Attribution Engine
- Per-branch & per-task model spend SQLite ledger
- Attention-leak audit & context pruning optimization
- Local Cockpit dashboard & context drift notifications
- Zero cloud dependencies (operates 100% on workstation)
Fleet Sovereign Governance
Engineering fleets (>5 developers), CISOs, CTOs & high-compliance enterprises.
Bespoke SLA & dedicated advisory
- Everything in Pro across entire engineering fleet
- Multi-repo GitOps push (
sprawl ws pushacross 40+ repos) - Centralized in-VPC telemetry & security gate enforcement
- EU AI Act (Art. 14), DORA & NIS2 compliance attestation
- Zero-trust CI/CD compliance gate integration
- Fractional Head of AI Advisory & Custom SLAs
The €100k/Year Secure AI Enablement Package (excl. VAT)
Unlock AI developer velocity (VS Code, IntelliJ, Cursor, Visual Studio) company-wide without security risk. Get up to 400 seat licenses, a self-hosted telemetry server (sprawl.telemetry) in your VPC, and a 3-day onsite CISO blueprinting and policy mapping workshop.
The 30-Day Security Integrity Guarantee
We guarantee deterministic workspace policy enforcement. If your team discovers that Sprawl fails to compile and enforce your declared repository rules within 30 days, we refund 100% of your software license fee.*
*Subject to pre-agreed technical parameters. Professional services and travel fees are non-refundable.
Forward to your security team → sprawl.software/team
"Velocity without governance is just technical debt generation. The data proves it. The GitClear study shows that while AI speeds up typing, it triggers a 2x increase in code churn. We enforce deterministic context boundaries and GitOps rules at the workstation before a single token is burned."
- Younes Baghor, Founder & Systems Architect
Frequently Asked Questions
Common questions regarding team rollout, workspace governance, and compliance evidence.
What is Sprawl.software?
Sprawl.software is the workstation governance and telemetry layer for autonomous AI coding agents. We act as the local compliance fabric, giving enterprises directory-scoped workspace governance and out-of-band audit trails without forcing you to use external cloud logins.
Does Sprawl make us SOC2 compliant?
No tool grants SOC2 certification. What Sprawl provides is the continuous audit trail that SOC2 auditors require as evidence: timestamped logs of every AI agent session, file access patterns, rules compliance rates, and tool execution history. Our telemetry output maps directly to SOC2 CC6.1 (logical access controls) and CC7.2 (system monitoring) criteria. Your auditor gets a queryable database, not a stack of self-reported questionnaires.
How does the out-of-band telemetry work?
Instead of intercepting network payloads or installing sluggish proxy servers, Sprawl harvests session telemetry out-of-band on the developer workstation. It parses prompt timelines, context coverage, and thinking steps with zero editor lag.
Where is my session telemetry data stored?
Your code, prompts, and credentials stay entirely behind your corporate firewall. Sprawl aggregates all telemetry in a local encrypted database and pushes it exclusively to a self-hosted Sprawl dashboard inside your private VPC. No code or keys ever touch Sprawl clouds.
What is the difference between Sprawl and Atomic Agentic Fabric (AFF)?
AFF is the open-source specification and schema layout format (declaring rules, workflows, and personas). Sprawl.software is the commercial governance engine and compliance cockpit that reads those schemas, synchronizes multi-IDE bindings, and audits local telemetry.
How is directory-scoped tool fencing enforced?
Fencing is enforced via a local MCP server that acts as a file operations provider for the agent. When an agent requests a file path read or write, the server validates that the target path is mathematically resolved within the allowed repository workspace root before permitting tool execution.